

Score third-party and open-source models and MCP servers for trust, vulnerabilities, and license risk before they reach underwriting or claims.
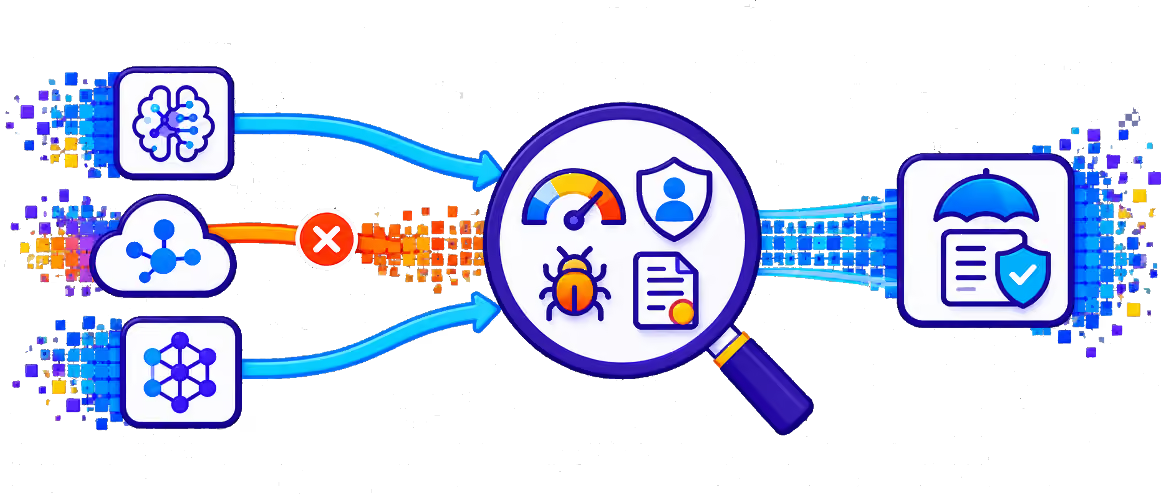
Carriers increasingly build underwriting and claims tools on third-party models, open-source components, and vendor services. Vendors may withhold documentation, treat outputs as a black box, and change model behavior without notice. PointGuard AI evaluates these components before and after adoption, giving insurers evidence about what they depend on and when that dependency changes.
Insurers remain accountable for outcomes produced by models they did not build and cannot fully inspect.
Supply Chain Security and AI Red Teaming evaluate third-party components and track how their risk changes over time.
1. Inventory AI dependencies. Identify models, datasets, libraries, and MCP servers used across underwriting, claims, and service applications. Generate an AI bill of materials for each system.
2. Score component risk. Evaluate publisher reputation, known vulnerabilities, unsafe file formats, and license terms. Flag components that fail the carrier's acceptance criteria before deployment.
3. Test vendor behavior. Run adversarial and harmful-output probes against third-party models in the carrier's own context. Document results for vendor reviews and model approval decisions.
4. Watch for changes. Re-score components and retest models when versions change. Alert owners when a dependency's risk rises so the carrier can respond before outcomes are affected.