

Risk-score the models, packages, and MCP servers your coding assistants rely on, and generate AI-BOMs before code reaches production.
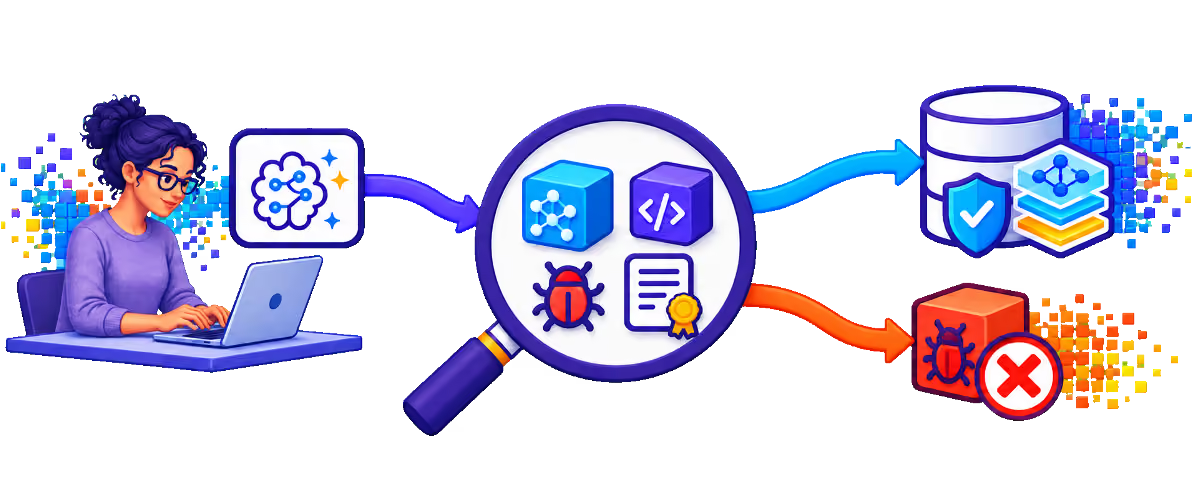
Coding assistants and agents pull suggestions, packages, and context from open-source models, public repositories, and MCP servers. An unvetted component can introduce vulnerabilities, license conflicts, or malicious payloads straight into a merge request. PointGuard AI evaluates the AI components engineering teams depend on and documents them in an AI bill of materials, so security teams know what is in the pipeline before it ships.
The AI supply chain behind coding tools changes daily and is rarely reviewed.
Supply Chain Security and AI Discovery & Inventory evaluate coding AI components and track their risk over time.
1. Discover coding AI. Identify coding assistants, agents, models, plugins, and MCP servers across developer endpoints, repositories, and CI/CD pipelines.
2. Score each component. Evaluate publisher reputation, known vulnerabilities, unsafe file formats, and license terms. Flag components that fail engineering acceptance criteria.
3. Generate AI-BOMs. Document the models, datasets, libraries, and MCP servers behind each application so security and legal teams can review dependencies.
4. Gate and monitor. Block high-risk components before deployment, re-score when versions change, and alert owners when a dependency's risk rises.