

Unify AI inventory, risk scores, and compliance evidence in one view for boards and retail partners.
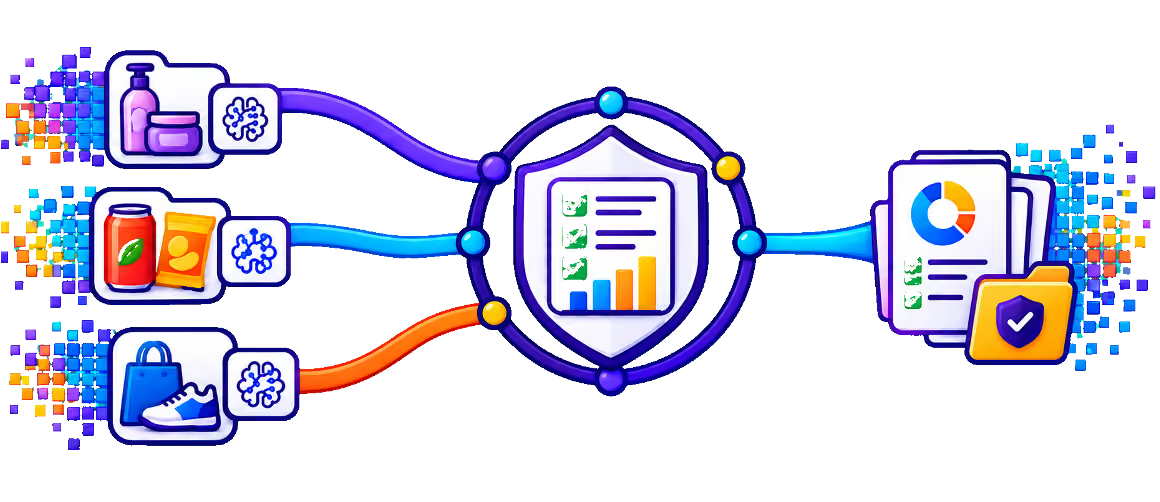
Boards, regulators, and retail partners increasingly ask how CPG companies govern AI. Ownership, risk scores, and evidence live in disconnected spreadsheets across brands and regions, so answers are slow and inconsistent. PointGuard AI unifies AI inventory, risk, and compliance evidence in one dashboard mapped to OWASP, NIST AI RMF, and GDPR.
AI governance evidence is fragmented across brands and regions.
AI Governance, AI Security Posture Mgt., and AI Discovery & Inventory centralize evidence and reporting.
1. Inventory AI across brands. Maintain a current list of AI systems, owners, and data access by brand and region.
2. Score risk consistently. Combine posture findings, test results, and runtime detections into one risk score per system.
3. Map to frameworks. Link controls and evidence to OWASP, NIST AI RMF, ISO/IEC 42001, and GDPR.
4. Report with confidence. Give boards and partners a current, consistent view of AI risk and remediation.
PointGuard AI supports governance programs; it does not by itself establish compliance with any regulation.