

Inventory every AI tool, agent, and MCP server your people actually use, including free consumer apps touching client documents.
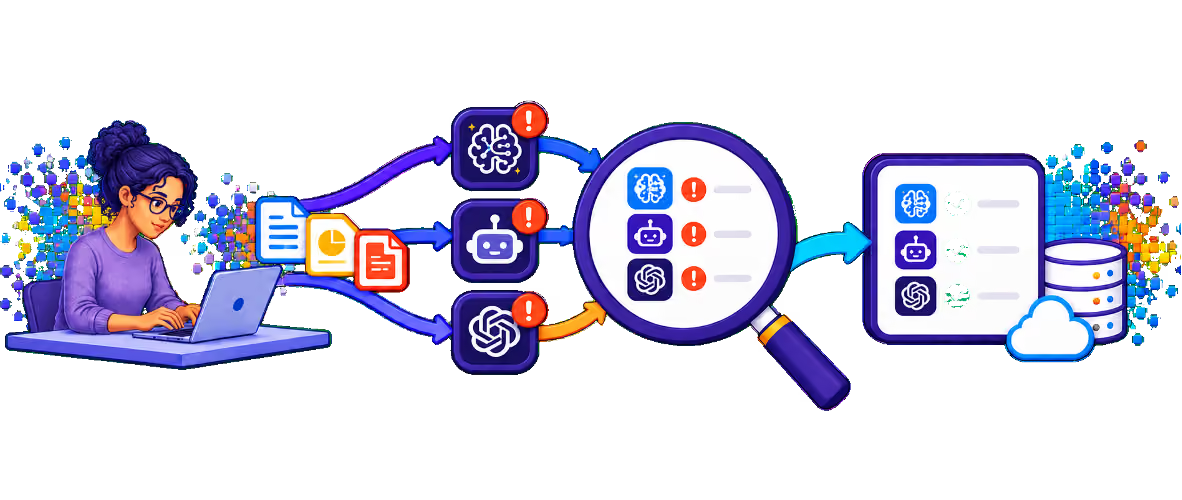
Associates and staff upload client documents into free consumer AI apps outside any firm-managed environment. IT cannot see these tools, and the firm cannot confirm whether client data has been stored or reused. PointGuard AI continuously inventories AI tools, agents, and MCP servers across clouds, repositories, and endpoints, giving risk teams the visibility to approve, restrict, or block them.
Shadow AI puts client confidentiality at risk without anyone noticing.
AI Discovery & Inventory and Shadow AI Control give firms a complete view of AI use and enforce acceptable use.
1. Discover across vectors. Scan endpoints, browsers, network traffic, SaaS integrations, and clouds for AI tools and agents.
2. Build one inventory. Record owner, practice group, data access, and vendor terms for each tool.
3. Decide and enforce. Approve, restrict, or block tools, and steer staff toward firm-approved alternatives.
4. Keep it current. Rescan continuously and report usage trends to risk committees.