

Run continuous adversarial and fairness testing on utilization management models and agents before skewed decisions reach patients.
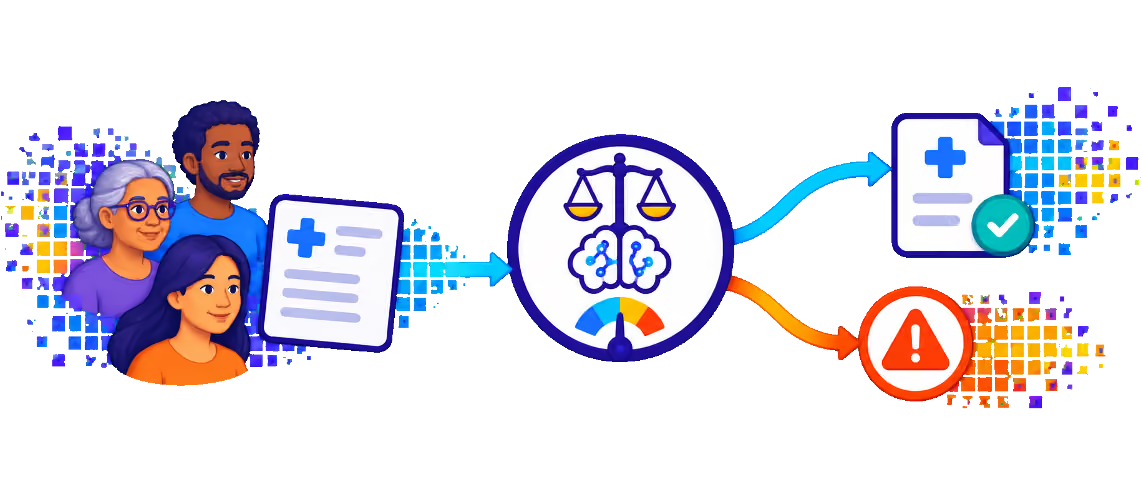
Prior authorization and utilization management agents now issue coverage recommendations at scale. Without adversarial and fairness testing, skewed or manipulated outputs can reach patients and providers before anyone reviews them, and regulators are increasingly scrutinizing automated denials. PointGuard AI tests these models continuously, documents results, and enforces human review where decisions affect care.
Automated coverage decisions carry clinical, regulatory, and reputational risk.
AI Red Teaming, Agent Mission Control, and AI Governance test models and keep humans in control of consequential decisions.
1. Define test scenarios. Build probe sets for authorization requests across service types, patient populations, and documentation patterns, with criteria set by clinical and compliance teams.
2. Test continuously. Run adversarial and fairness probes on a schedule and after every model, prompt, or policy change. Compare results across versions to detect regressions.
3. Enforce human review. Require clinician approval before an agent issues a denial or other adverse determination.
4. Document results. Map findings to OWASP and NIST AI RMF and keep a reviewable record for governance committees and regulators.
Adversarial testing complements clinical review and statistical fairness analysis; it does not replace either.