

Apply financial content policies to AI responses before unsupported rates or restricted advice reach banking customers.
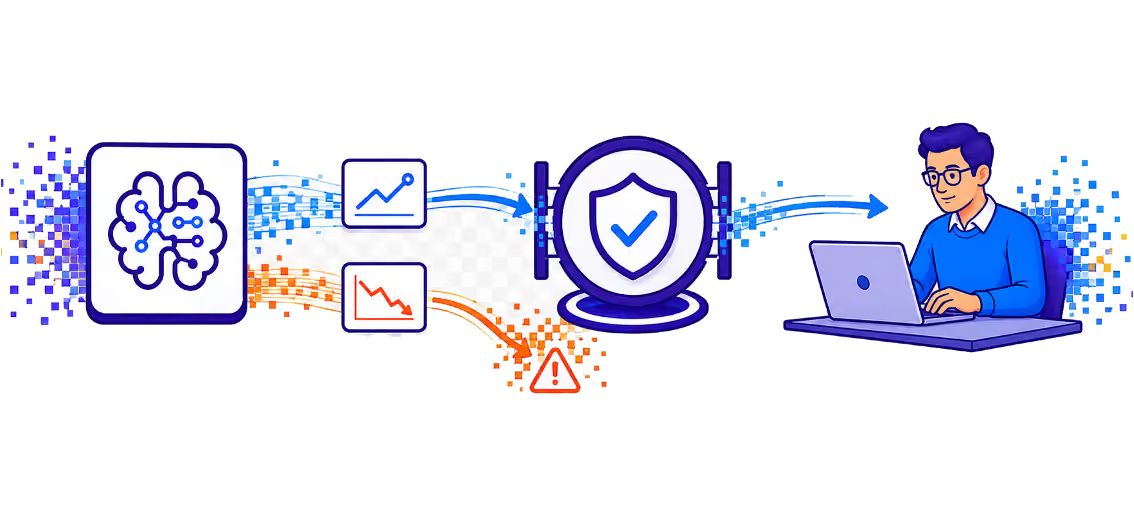
A banking chatbot can present a fabricated interest rate or investment recommendation with the same confidence as an approved answer. Customers may act on that output before anyone reviews it. PointGuard AI combines adversarial testing with runtime guardrails to identify failure patterns, enforce content restrictions, and block policy violations in customer-facing AI interactions.
Fluent AI responses can conceal unsupported financial statements and create misplaced confidence in automated guidance.
PointGuard AI uses AI Red Teaming and Runtime Guardrails to test financial response behavior and enforce bank-defined content boundaries.
1. Test financial scenarios. Probe chatbots with questions about rates, products, investments, and prohibited recommendations. Review the exact prompts, responses, and failures before approving a model or application for use.
2. Define response boundaries. Establish policies for restricted advice, unsafe content, and permitted customer interactions. Apply context such as application exposure, business unit, and risk to enforcement decisions.
3. Enforce output policies. Inspect generated responses before delivery. Block responses that violate configured rules, and record or alert on detected issues so teams can investigate recurring failure patterns.
4. Monitor and retest. Track violations and repeat assessments as prompts, models, or applications change. Use the findings to refine policies and identify interactions that require additional review.
These controls reduce exposure to unsafe financial content; factual rate verification still requires the application to use approved, current banking data.