

Verify agent identities and delegated authority before allowing sensitive payment actions across banking tools and workflows.
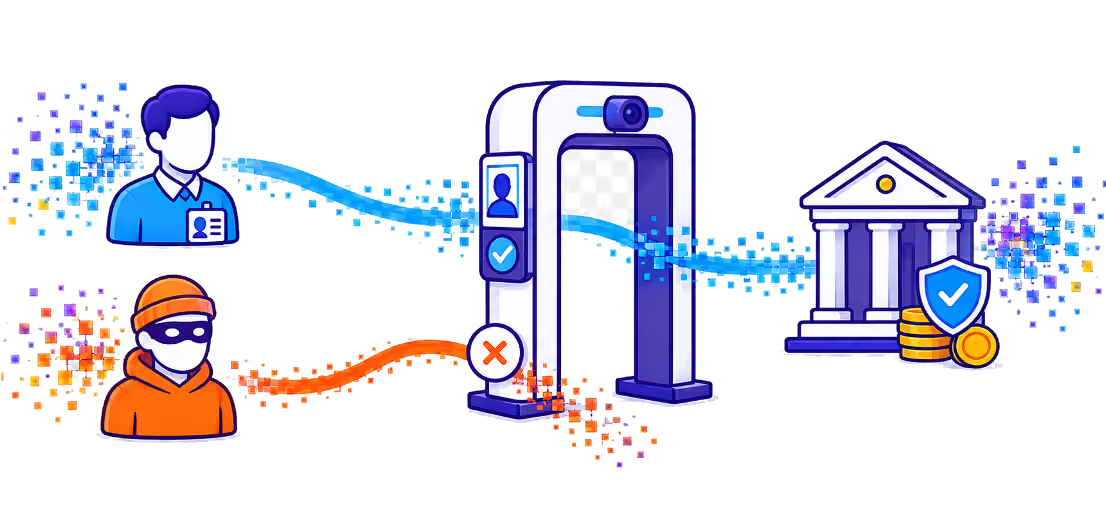
A payment request can appear legitimate while originating from an impersonated agent, misused credential, or manipulated workflow. Banks need to validate both who an agent is and whether its proposed action fits its authorized purpose. PointGuard AI binds agents to verifiable identities and applies action-level policies, helping prevent unauthorized payment activity across connected financial systems.
A valid connection or familiar agent name does not prove that a payment instruction is authorized.
Agent Identity & Access Security, Agent Mission Control, and MCP Security Gateway combine identity verification with contextual authorization and pre-execution controls.
1. Establish verifiable identities. Bind each agent to a cryptographic identity, named owner, mission, and access scope. Distinguish approved agents from unknown identities before granting access to banking tools or workflows.
2. Validate delegated authority. Preserve the initiating user's identity and authorization context across agent interactions. Evaluate the requested operation and target resource against both agent permissions and delegated user authority.
3. Check payment actions. Apply bank-defined rules before a governed payment operation executes. Block requests outside the approved scope or require human approval for sensitive actions, exceptions, and elevated risk.
4. Investigate and contain misuse. Correlate identity claims, tool activity, behavioral deviations, and policy results. Use agent containment and access restrictions to limit further activity while security teams investigate suspicious requests.