

Protect policyholder PII, claims files, and medical records across chatbots, copilots, and agent tool calls.
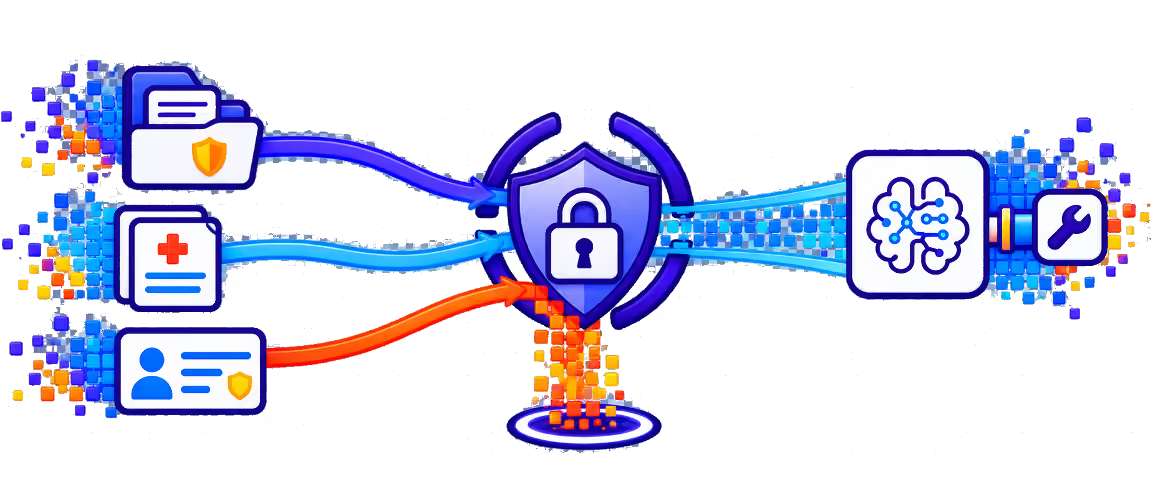
Claims adjusters, underwriters, and service agents now move claims files, medical records, and policyholder PII through AI prompts, model responses, and MCP tool calls. Traditional DLP inspects files and email, not these interactions. PointGuard AI applies data protection policies at each AI interaction point, helping carriers keep regulated data within approved boundaries while teams continue to use AI.
Regulated insurance data can leave approved systems through AI channels that existing controls do not inspect.
AI Data Protection, Runtime Guardrails, and MCP Security Gateway enforce data policies across AI workflows.
1. Define protected data. Identify policyholder PII, claims records, health information, and carrier-specific identifiers. Set rules for permitted uses and destinations by line of business.
2. Inspect AI interactions. Scan prompts, responses, and governed MCP tool calls for protected data before it reaches a model, user, or external service.
3. Redact or block exposure. Mask sensitive fields when work can safely continue. Block interactions that would send protected data to an unapproved destination.
4. Record enforcement evidence. Log detections and actions for privacy, compliance, and incident response teams. Map detections to HIPAA, GLBA, and GDPR obligations for reporting.