

Detect source code, customer data, and product IP in prompts, responses, and tool calls before it leaves approved AI tools.
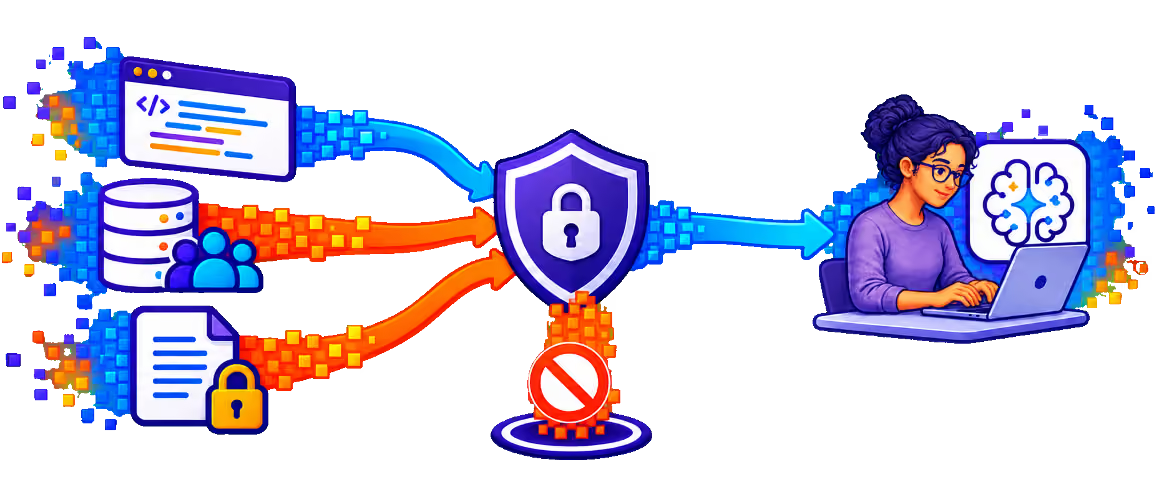
Engineers paste source code and logs into public AI assistants, while business teams share customer records, contracts, and roadmaps with chatbots and copilots. Traditional DLP does not inspect these interactions, so sensitive data leaves the company without a trace. PointGuard AI applies AI-native data protection across prompts, responses, and tool calls, keeping code and customer data within approved boundaries.
Sensitive technology data moves through AI tools that existing DLP cannot see.
AI Data Protection and Shadow AI Control enforce data policies across sanctioned and unsanctioned AI tools.
1. Define protected data. Use built-in detectors for PII, credentials, and source code, and add custom types for product names, repositories, and roadmaps.
2. Inspect every interaction. Scan prompts, responses, and governed tool calls at sub-100 ms latency across browsers, IDEs, and AI applications.
3. Redact, block, or redirect. Mask sensitive data when work can continue, block it when it cannot, and steer users toward approved AI tools.
4. Report and refine. Track detections by team and tool, and feed events into security operations and policy updates.