

Replace static keys with authenticated, scoped access for business associates and MCP-connected claims and billing tools.
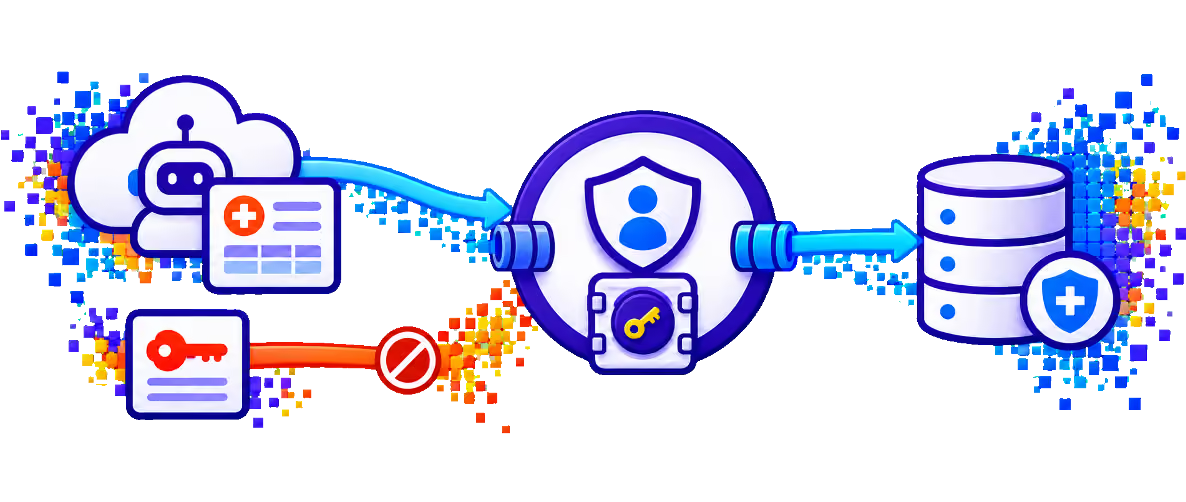
Business associates and MCP-connected claims and billing tools often authenticate with static API keys and shared credentials. A single vendor compromise can expose millions of patient and claims records, as recent healthcare breaches have shown. PointGuard AI brings identity, secrets management, and per-tool authorization to these connections so payers and providers can govern vendor access with the same rigor as their own systems.
Vendor integrations hold broad, long-lived access to claims and patient data.
Agent Identity & Access Security and MCP Security Gateway authenticate vendor agents and authorize every governed tool call.
1. Inventory vendor connections. Identify business associate agents, MCP servers, and the claims, billing, and EHR systems they reach. Record owners and contracted purpose.
2. Authenticate every agent. Replace static keys with OAuth 2.0 and short-lived, scoped tokens. Broker secrets through HashiCorp Vault, AWS Secrets Manager, or Azure Key Vault.
3. Authorize each tool call. Grant access by agent, tool, operation, and record type. Separate read from write and inspect traffic for PHI and threats.
4. Monitor and review. Trace tool calls and policy decisions per vendor. Feed evidence into business associate oversight and revoke access quickly when a vendor is compromised.