

Discover external agents and MCP connections, restrict their access, and inspect interactions with sensitive banking systems.
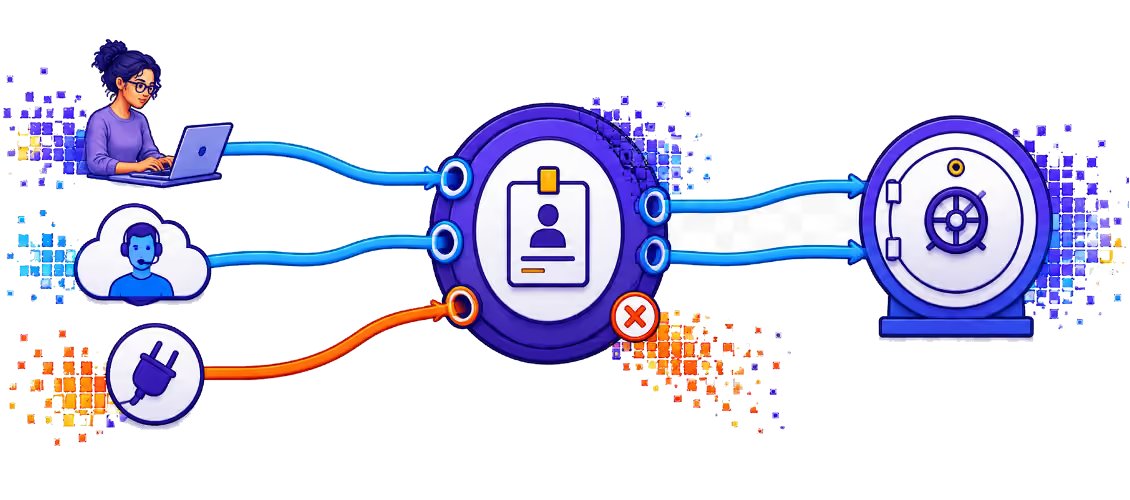
Vendor agents and MCP-connected services can reach customer records, internal applications, and financial operations through integrations owned by different business teams. Banks need to know what those agents can access and how their authority is constrained. PointGuard AI combines discovery, identity controls, and gateway enforcement to govern third-party connections alongside internally developed agents.
External AI integrations expand access to banking systems faster than security teams can inventory and govern them.
PointGuard AI inventories agent connections and applies MCP Security Gateway and Agent Identity & Access Security controls to the tools and resources they reach.
1. Discover connected assets. Identify agents, MCP servers, tools, endpoints, and their relationships. Establish ownership and review which vendor connections can reach customer data or sensitive bank applications.
2. Verify identity and delegation. Authenticate agents and preserve the user context behind delegated requests. Apply on-behalf-of access controls so an integration's technical connectivity does not become unrestricted banking authority.
3. Constrain tool operations. Authorize access by agent, tool, operation, and resource. Separate read and write privileges, require approval where appropriate, and inspect governed interactions for threats and sensitive information.
4. Monitor integration activity. Trace tool calls, policy decisions, and delegation chains. Use the resulting evidence to investigate anomalous vendor activity and refine access as an integration's purpose or risk changes.