

Protect sensitive financial information across customer chatbots, employee copilots, and agent workflows without disrupting approved work.
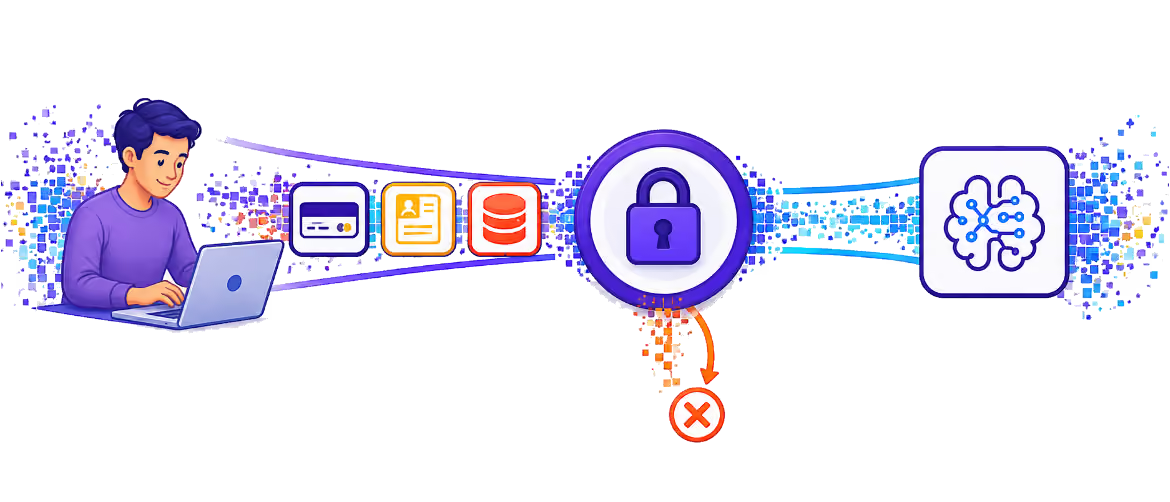
Customer service assistants, loan officers, and financial agents routinely handle account numbers, Social Security numbers, balances, and payment information. That data can travel through prompts, generated responses, retrieved documents, and connected tools. PointGuard AI applies data protection policies at these interaction points, helping banks keep sensitive information within approved boundaries while employees and customers continue using AI.
Financial data can leave approved systems through AI interactions that existing controls do not consistently inspect.
PointGuard AI combines AI Data Protection, Runtime Guardrails, and MCP Security Gateway controls to enforce financial data policies across AI workflows.
1. Define sensitive data policies. Identify account details, payment information, personal identifiers, and bank-specific data that require protection. Set rules for permitted uses, destinations, and enforcement actions.
2. Inspect AI interactions. Scan prompts and responses for sensitive information, and inspect data moving through governed MCP tool calls. Apply policies before restricted content reaches a model, user, or connected service.
3. Redact or block exposure. Mask or redact sensitive fields where work can safely continue. Block interactions that exceed policy, including requests to send protected information to an unapproved destination.
4. Preserve enforcement evidence. Record detections, policy decisions, and actions for investigation and oversight. Give security teams a consistent view of financial data exposure across protected AI channels.