

Authenticate vendor agents, restrict their access to claims and policy systems, and inspect every connected tool call.
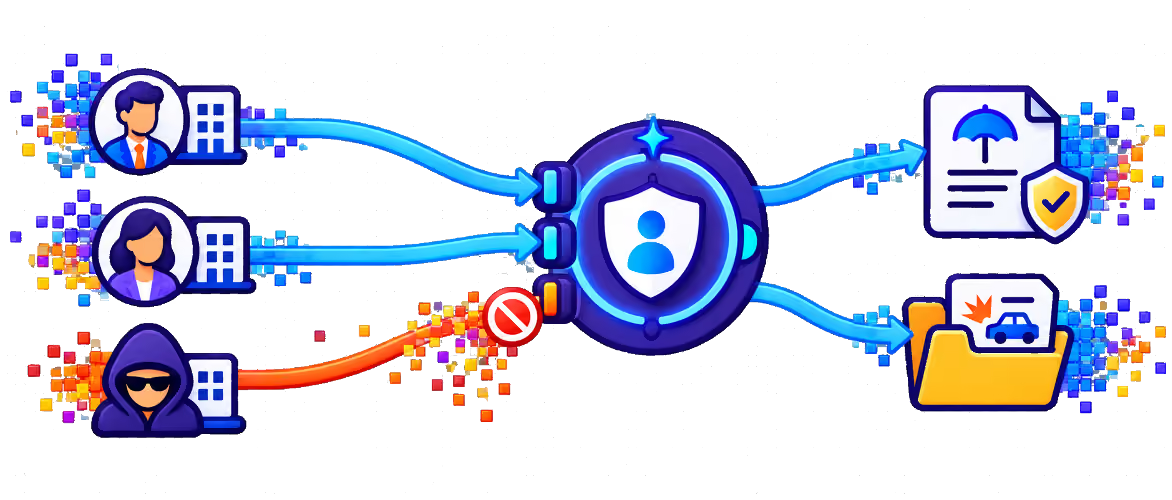
Vendor-supplied copilots and agents increasingly connect to policy administration, claims, and rating systems through MCP servers and APIs. Many of these integrations ship with static keys and broad permissions, so a compromised vendor tool can read or alter claims data without anyone noticing. PointGuard AI brings discovery, identity, and gateway enforcement to these connections so carriers can govern third-party access alongside their own agents.
Vendor integrations reach core insurance systems faster than security and vendor risk teams can review them.
PointGuard AI inventories vendor connections and applies MCP Security Gateway and Agent Identity & Access Security controls to every governed tool call.
1. Discover vendor connections. Identify vendor agents, MCP servers, tools, and the claims, policy, and rating systems they can reach. Assign an owner and record the business purpose for each connection.
2. Authenticate every agent. Replace static keys with OAuth 2.0 flows and short-lived, scoped tokens. Preserve the user context behind delegated requests so vendor connectivity never becomes standing access.
3. Authorize each operation. Grant access by agent, tool, operation, and resource. Separate read from write, require approval for claim changes or payments, and inspect tool traffic for sensitive data and threats.
4. Monitor and review vendors. Trace tool calls, policy decisions, and delegation chains for each vendor. Feed the evidence into third-party risk reviews and tighten access when a vendor's scope or risk changes.