

Maintain a current AI inventory, documented controls, and audit-ready evidence that state insurance examiners can review.
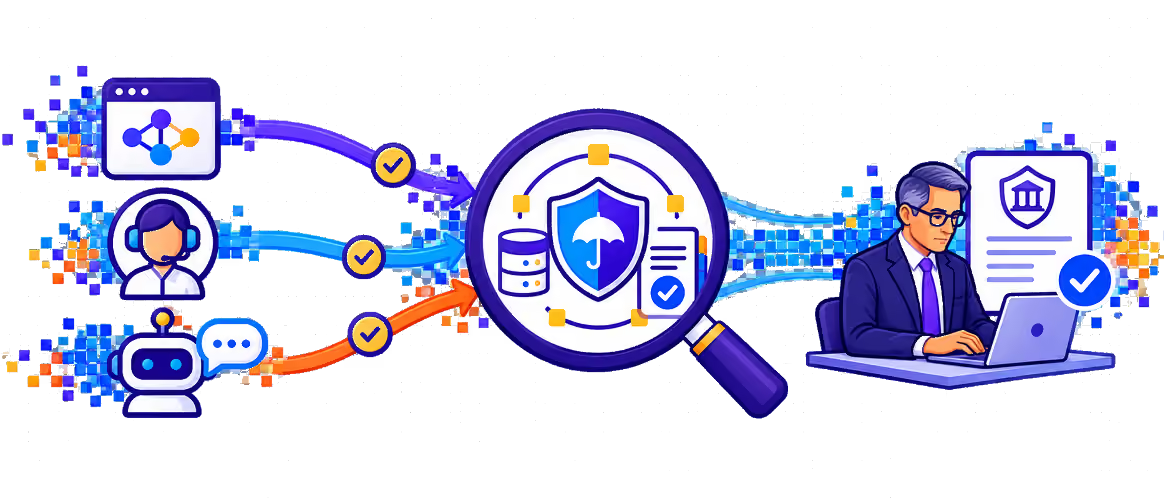
State regulators, following the NAIC Model Bulletin on insurers' use of AI, expect carriers to maintain a written AI program, an accountable owner for each system, and evidence that controls work. Most insurers assemble that evidence by hand from spreadsheets kept by underwriting, claims, and IT teams. PointGuard AI centralizes inventory, testing results, and policy enforcement records so governance teams can answer examiner requests with current, consistent evidence.
Governance evidence is scattered across teams, so it is incomplete by the time an examiner asks for it.
AI Governance, AI Discovery & Inventory, and AI Security Posture Mgt. combine discovery, risk scoring, and framework mapping into one governance record.
1. Build a complete inventory. Discover models, applications, agents, and MCP servers across clouds, code repositories, and runtime telemetry. Record owners, business use, and the policyholder data each system touches.
2. Assess and score risk. Combine posture findings, adversarial testing results, and runtime detections into a risk score for each AI system. Prioritize high-impact uses such as underwriting, pricing, and claims decisions.
3. Map controls to frameworks. Link findings and enforcement records to NIST AI RMF, OWASP, and ISO/IEC 42001. Organize evidence by system so it supports state examination requests and internal audit.
4. Report continuously. Use dashboards and exports to show inventory changes, open risks, and remediation progress. Keep governance committees and regulators working from the same current record.
PointGuard AI supports a carrier's AI governance program; it does not replace legal review or establish compliance with any specific state requirement.