

Treat every retrieved ticket, document, and tool output as untrusted, and block hidden instructions before they reach the model.
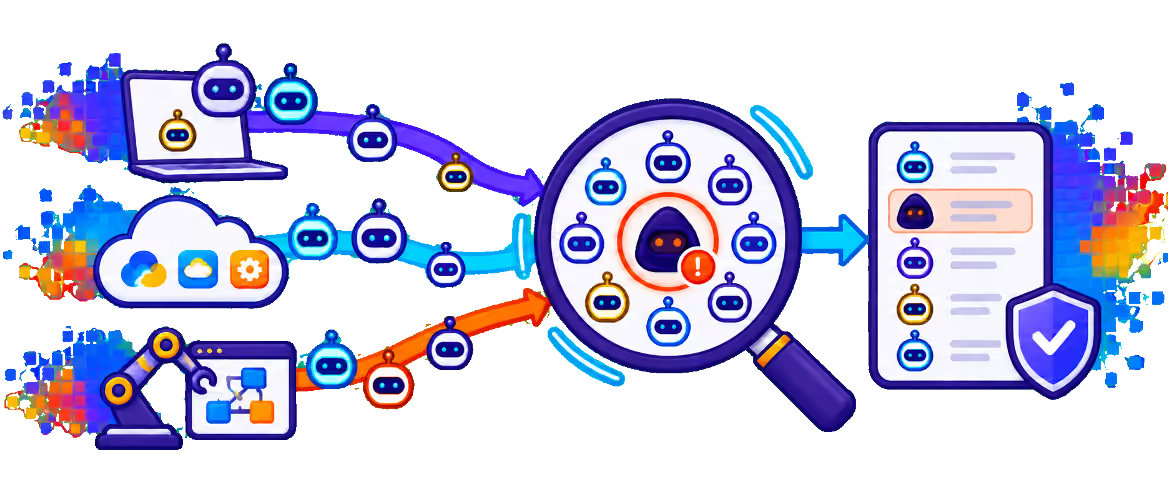
Support and knowledge agents retrieve tickets, emails, and documents that customers and outsiders can write. Attackers seed that content with hidden instructions that make agents leak data, change records, or act outside their scope. PointGuard AI inspects retrieved content and tool outputs before they reach the model and tests agents against injection techniques before release.
Anyone who can submit a ticket can try to steer a support agent.
Runtime Guardrails and AI Red Teaming test support agents and block injected instructions at runtime.
1. Inspect retrieved content. Scan tickets, documents, and tool outputs for injection patterns using fine-tuned detection models at sub-100 ms latency.
2. Enforce response policies. Block responses that reveal other customers' data, system prompts, or restricted information.
3. Constrain actions. Limit which tools a support agent can call and require approval for record changes triggered by retrieved content.
4. Test continuously. Probe agents with direct and indirect injection scenarios before release and after every model or prompt change.