

Replace static API keys in code with short-lived, scoped OAuth tokens per agent, and broker remaining secrets through a vault.
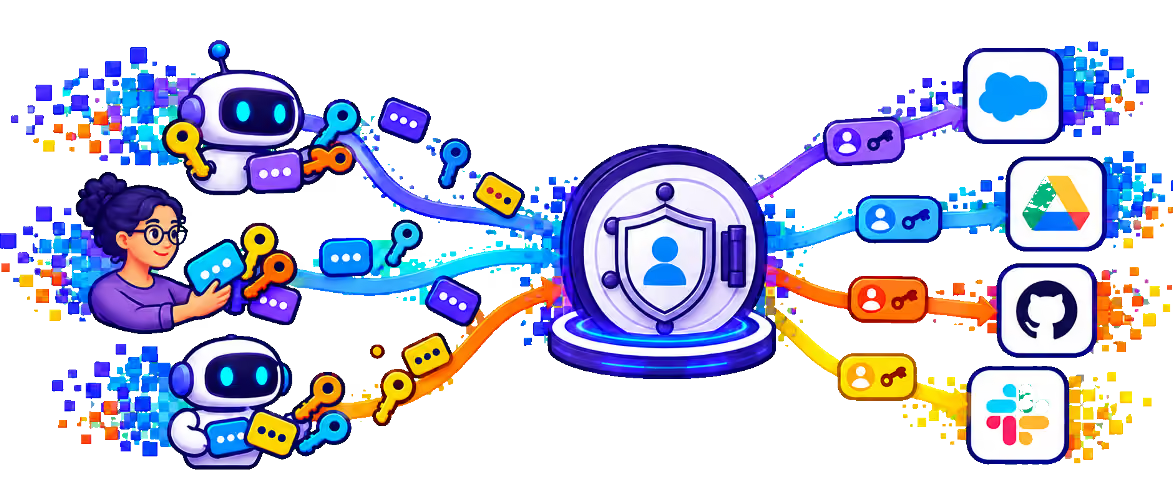
LLM and MCP integrations in SaaS products often rely on static API keys embedded in code or configuration. One leaked credential can expose every tenant's data and is hard to rotate without downtime. PointGuard AI issues each agent short-lived, scoped OAuth 2.0 tokens and brokers secrets through enterprise vaults, eliminating static keys from agent integrations.
Static credentials turn a single leak into a multi-tenant breach.
Agent Identity & Access Security replaces static keys with scoped, short-lived credentials per agent.
1. Find static credentials. Discover API keys and tokens used by agents and MCP integrations across code, configs, and runtime.
2. Issue scoped tokens. Grant each agent short-lived OAuth 2.0 tokens limited to the tenant, tools, and operations it needs.
3. Broker secrets. Store and inject remaining secrets through HashiCorp Vault, AWS Secrets Manager, or Azure Key Vault instead of code.
4. Rotate and revoke. Rotate credentials automatically and revoke a single agent's access instantly when compromise is suspected.