

Enforce per-agent, per-tool, per-operation authorization on every MCP call, and route high-risk operations for human approval.
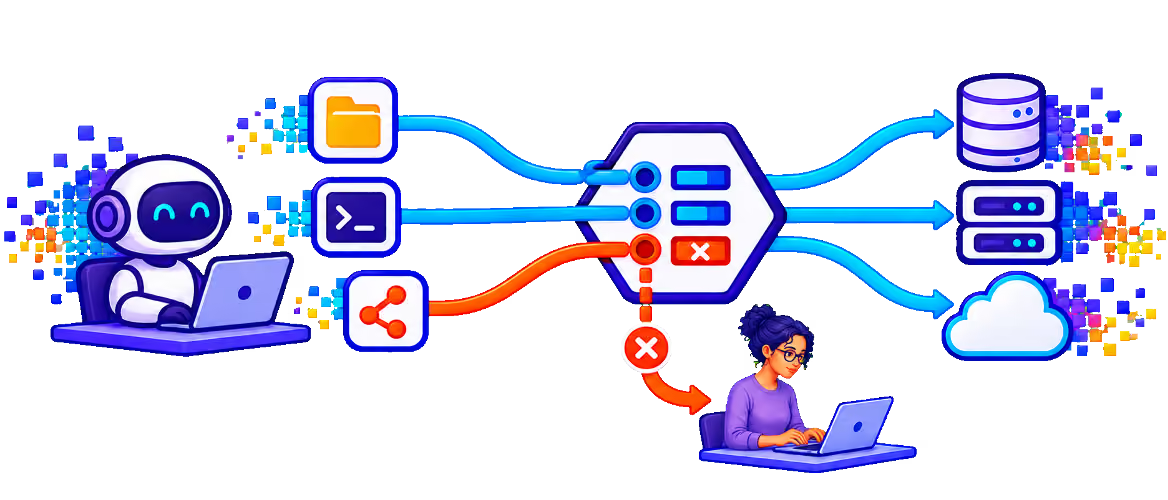
Engineering and support agents now connect to dozens of internal MCP servers that expose file systems, code execution, databases, and internal APIs. Most of these connections grant broad access by default, so a manipulated agent can reach far more than its task requires. PointGuard AI inventories MCP servers and enforces fine-grained authorization on every governed tool call.
MCP adoption outpaces the controls that should govern it.
MCP Security Gateway and AI Discovery & Inventory bring visibility and least-privilege control to internal MCP ecosystems.
1. Discover MCP servers. Inventory internal and third-party MCP servers, the tools they expose, and the agents connected to them. Score each server for risk.
2. Authorize every call. Define policies by agent, tool, operation, and resource. Separate read from write and restrict code execution and file system access to approved agents.
3. Require approval for high-risk operations. Route destructive or sensitive operations, such as production changes, to a human for approval before they run.
4. Inspect and log. Inspect tool requests and responses for sensitive data and injected instructions, and log every decision for investigation and audit.