

Require approval for sensitive financial actions while allowing routine agent work to continue within defined policy.
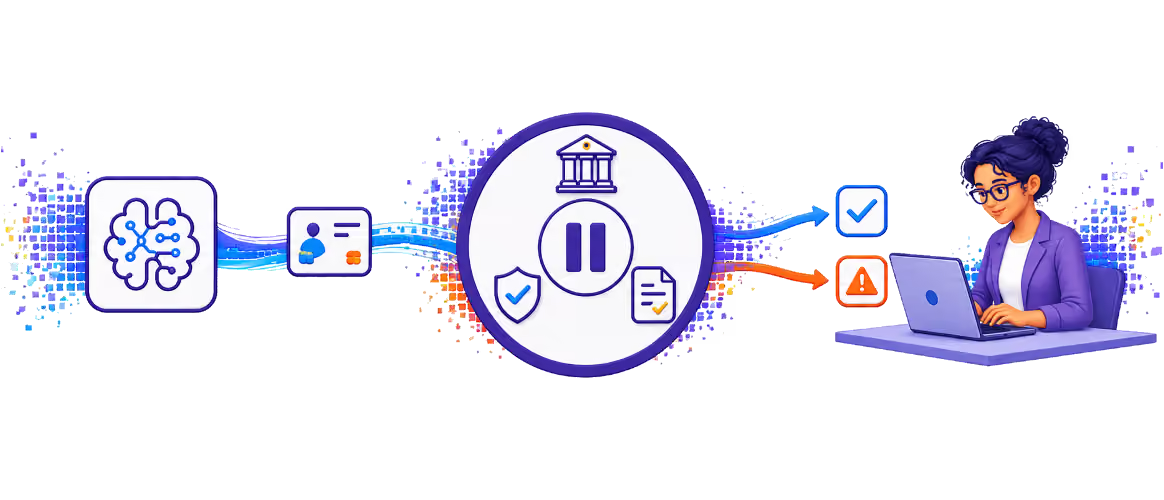
Lending and collections agents can recommend terms, update records, and initiate actions that affect customers. Banks need clear boundaries between tasks an agent may perform and decisions that require a person's approval. PointGuard AI evaluates actions before execution and supports human approval workflows, helping institutions retain oversight as automation moves into consequential financial processes.
Human review loses its value when it happens after an agent has already taken a consequential action.
Agent Mission Control and MCP Security Gateway apply policy checks and approval requirements at the point where an agent requests a sensitive action.
1. Define approval thresholds. Identify lending and collections operations that require human authorization. Distinguish routine record access from sensitive changes, financial commitments, or actions affecting a customer's treatment.
2. Evaluate each proposed action. Assess the agent, operation, target resource, delegated user authority, and policy context before execution. Block actions outside the approved scope and route eligible exceptions for human review.
3. Preserve the approval boundary. Require the configured approval or step-up authentication before a protected operation proceeds. Keep these controls outside the agent so generated instructions cannot waive the requirement.
4. Capture decisions and outcomes. Record requests, approvals, enforcement events, and resulting actions. Give reviewers and investigators a traceable record connecting the human decision to the agent's subsequent activity.