

Treat every data-room document and tool output as untrusted, and block hidden instructions before they redirect e-discovery agents.
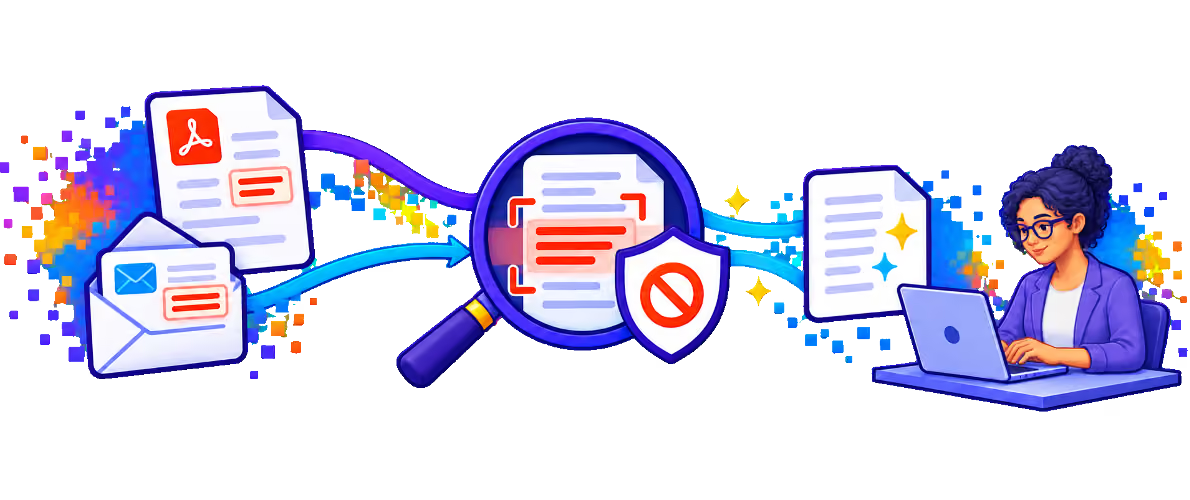
E-discovery and due diligence agents retrieve emails, contracts, and PDFs from data rooms supplied by clients and counterparties. Hidden instructions in those documents can redirect an agent's next action, skew a review, or exfiltrate privileged material. PointGuard AI scans retrieved content and tool outputs for injection patterns before they reach the model and constrains what agents can do afterward.
Firms routinely process documents written by adversaries.
Runtime Guardrails and AI Red Teaming block injected instructions and test review agents.
1. Inspect retrieved content. Scan documents, emails, and tool outputs for injection patterns using fine-tuned detection models at sub-100 ms latency.
2. Constrain agent actions. Limit which tools review agents can call after reading untrusted content.
3. Flag suspicious documents. Route documents with detected manipulation to reviewers.
4. Test continuously. Probe agents with injection scenarios before matters begin and after updates.