

Apply posture baselines and continuous adversarial testing to AI-enabled devices and the cloud platforms they connect to.
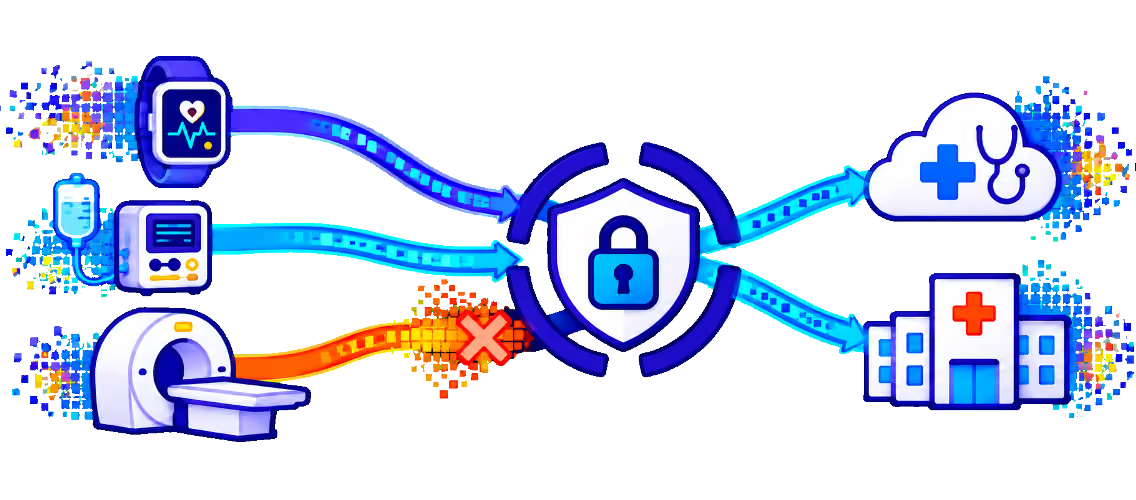
AI-enabled medical devices increasingly ship with embedded models, agents, and cloud connections. Testing often stops when a device leaves the lab, even as models update and new attack techniques emerge, and FDA expects manufacturers to manage cybersecurity across the product lifecycle. PointGuard AI applies posture management and continuous adversarial testing to device AI and its supporting cloud platforms.
Device AI must stay secure long after release, across many deployed versions.
AI Security Posture Mgt. and AI Red Teaming harden device AI and test it continuously.
1. Inventory device AI. Identify models, agents, and cloud services across device lines and versions, and generate an AI bill of materials for each.
2. Harden supporting platforms. Apply zero-trust baselines to the cloud and MLOps environments that train, update, and serve device models. Detect misconfigurations and credential sprawl.
3. Test continuously. Run adversarial probes against device models and agents on a schedule and before each update ships.
4. Track and report. Route findings to engineering owners and keep version-level evidence to support postmarket cybersecurity management and customer reviews.