

Turn AI policy into enforced controls mapped to OWASP, NIST AI RMF, and ISO/IEC 42001, consistently across practice groups.
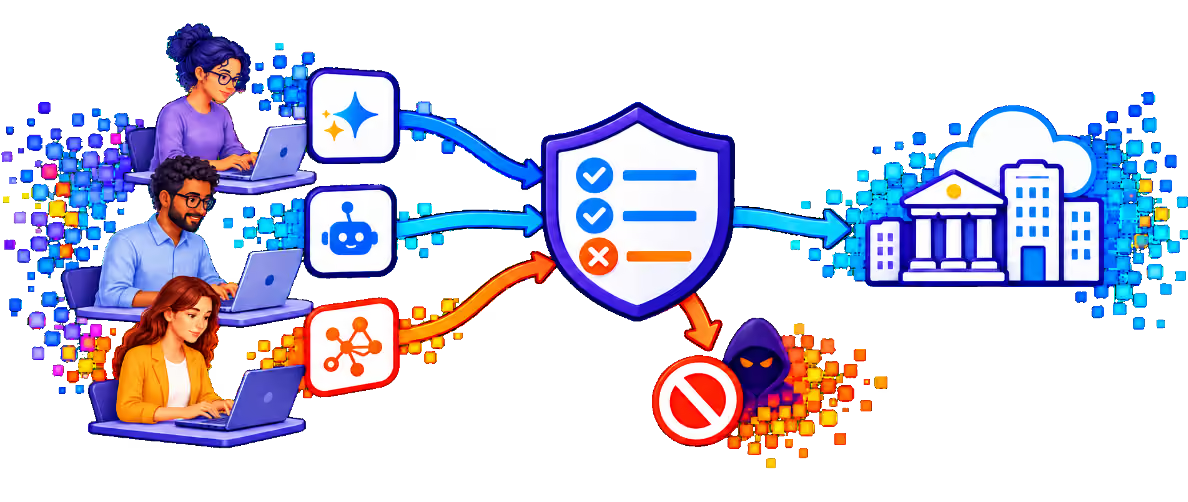
Many firms lack a formal generative AI policy, or have one that is not enforced, leaving each practice group to set its own rules for client data. Clients, insurers, and regulators increasingly expect firms to show how AI use is governed. PointGuard AI turns policy into enforced controls and maps every finding, control, and audit record to recognized frameworks.
AI policy is inconsistent and rarely enforced.
AI Governance, Shadow AI Control, and Runtime Guardrails turn policy into enforced, auditable controls.
1. Define firm-wide policy. Set acceptable use, data handling, and review rules, with practice-specific variations where needed.
2. Enforce in tools. Apply policies through discovery, data protection, and output guardrails.
3. Map to frameworks. Link every finding, control, and audit record to OWASP, NIST AI RMF, and ISO/IEC 42001.
4. Report and update. Show leadership and clients current compliance, and update policies as tools and rules change.