

Find every AI tool, browser extension, and agent touching patient data, including those adopted without a business associate agreement.
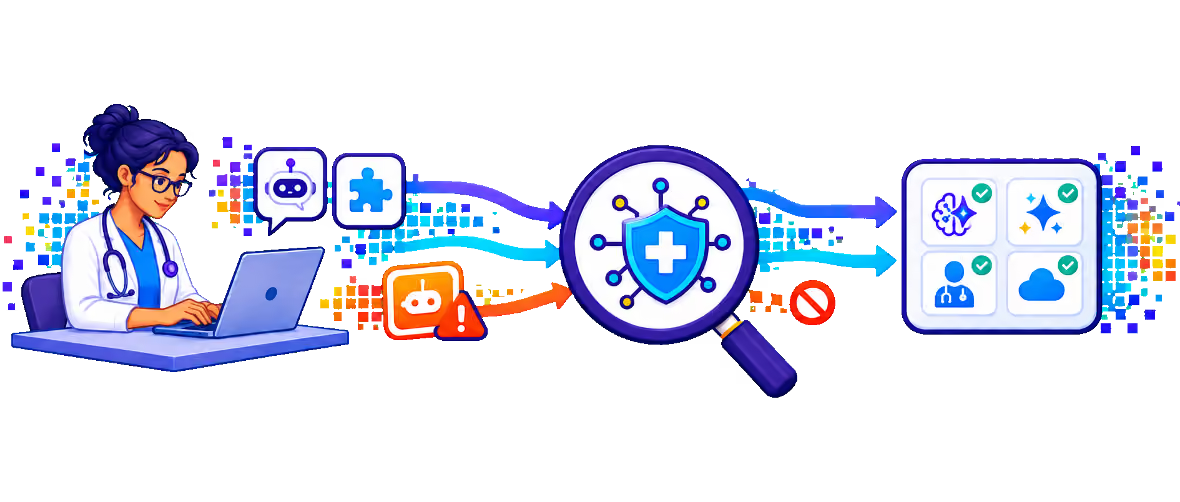
Clinicians and staff adopt AI writing tools, chatbots, and browser extensions on their own, often without a signed business associate agreement. Each one becomes a path for PHI to leave the organization, and none appear in the IT asset inventory. PointGuard AI discovers AI usage across clouds, SaaS, code, and endpoints, giving security and privacy teams one inventory to review, approve, or restrict.
Shadow AI spreads through care teams faster than security and privacy teams can review it.
AI Discovery & Inventory and Shadow AI Control build a continuous inventory and enforce acceptable use.
1. Discover across every vector. Scan cloud accounts, SaaS integrations, code repositories, network traffic, and endpoints for models, applications, extensions, and agents.
2. Build one inventory. Deduplicate findings into a single record per AI asset, with owner, department, data access, and vendor status, including whether a business associate agreement is in place.
3. Classify and decide. Flag tools that touch PHI without approval. Route each one for review, then approve, restrict, or block it under the organization's acceptable use policy.
4. Keep it current. Rescan continuously and alert owners when new AI tools appear, so the inventory reflects what care teams actually use.