

Inspect prompts, responses, and tool calls so customer PII and account data never cross tenant boundaries or reach unapproved LLMs.
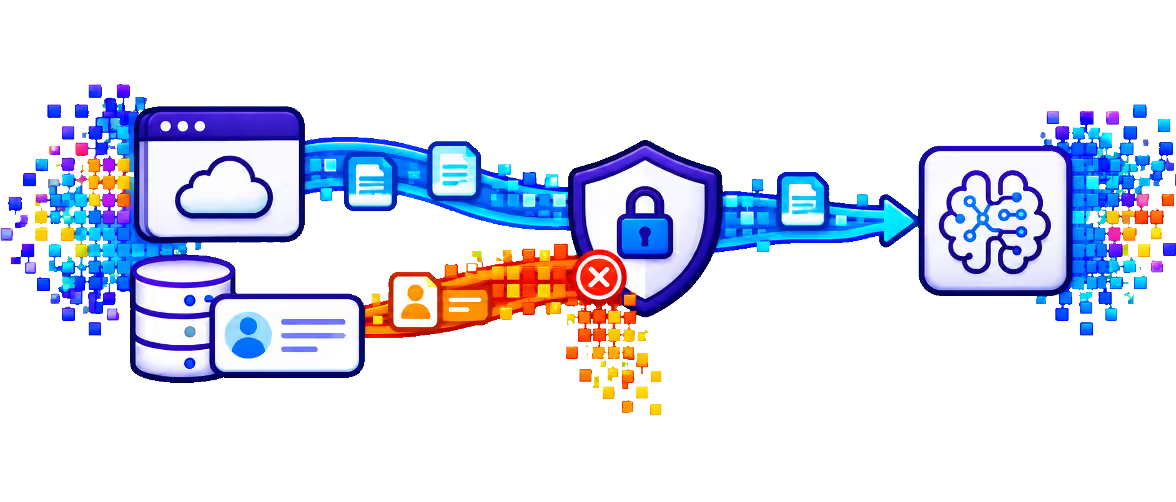
SaaS copilots and agents send customer PII, account records, and support history to third-party LLMs through prompts and MCP tool calls. A single retrieval or prompt-construction error can expose one tenant's data to another, and traditional DLP does not inspect these flows. PointGuard AI applies AI-native data protection inside the product so tenant data stays where it belongs.
Tenant data moves through AI pipelines that existing controls cannot see.
AI Data Protection, Runtime Guardrails, and MCP Security Gateway enforce data policies inside SaaS AI features.
1. Define protected data. Use built-in PII detectors and add custom types for account IDs, tenant identifiers, and customer-specific data.
2. Inspect every interaction. Scan prompts, responses, and governed MCP tool calls at sub-100 ms latency, without adding noticeable delay for users.
3. Enforce tenant boundaries. Block responses that contain data from another tenant and redact sensitive fields before they reach external models.
4. Prove isolation. Log detections and enforcement events per tenant to support customer reviews, SOC 2 audits, and incident response.