

Detect consumer PII and proprietary formulations in prompts, responses, and tool calls before they leave approved AI tools.
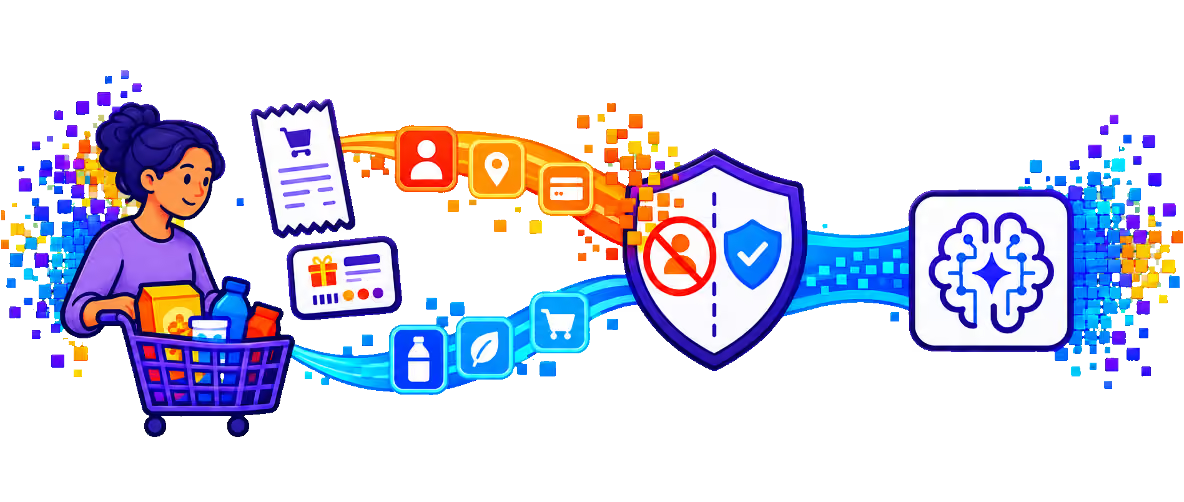
Marketing, consumer insights, and R&D teams paste survey data, loyalty records, and product formulations into copilots and chatbots. Legacy DLP does not inspect these interactions, and generic detectors do not recognize formulas or ingredient specifications. PointGuard AI applies AI-native data protection with custom detectors for consumer data and proprietary formulas across every AI interaction.
Consumer and product data moves through AI tools without inspection.
AI Data Protection and Shadow AI Control enforce data policies across sanctioned and unsanctioned AI tools.
1. Define protected data. Use built-in PII detectors and create custom types for formulas, ingredient specifications, and project code names.
2. Inspect every interaction. Scan prompts, responses, and tool calls at sub-100 ms latency.
3. Redact, block, or redirect. Mask sensitive data when work can continue, block it when it cannot, and steer users to approved tools.
4. Report by team and market. Track detections and feed events into privacy and IP protection programs.