

Give every audit, tax, and advisory agent its own cryptographic identity, so each action is attributable and access can be revoked instantly.
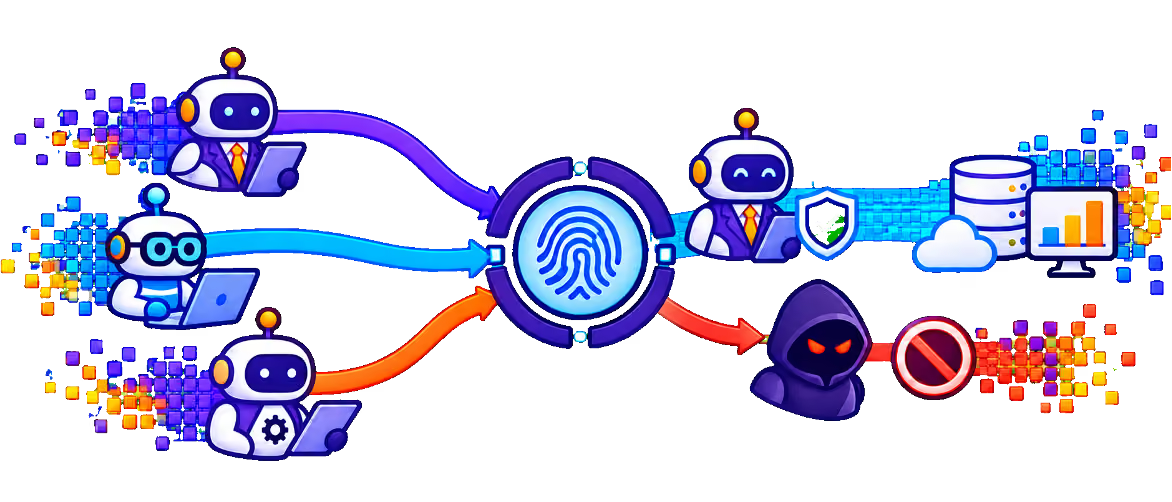
Consultancies run dozens of agents for audit sampling, tax research, and advisory analysis, and most inherit a consultant's own login. No action traces to a specific agent, access is far broader than the task, and revoking one agent means disrupting the consultant. PointGuard AI issues each agent a verifiable identity with scoped, delegated access.
Agents acting under personal logins cannot be attributed or contained.
Agent Identity & Access Security gives each agent a verifiable identity and scoped access.
1. Register every agent. Assign each agent a DID-based identity backed by Ed25519 signatures, with an owner and engagement scope.
2. Delegate with context. Use On-Behalf-Of tokens so actions carry both agent and consultant identity.
3. Scope to the engagement. Issue short-lived tokens limited to the client, engagement, and tools required.
4. Attribute and revoke. Tie every action to its agent and revoke any agent instantly.