

Connect agent identities, tool calls, policy decisions, and approvals in a traceable record for examiner review.
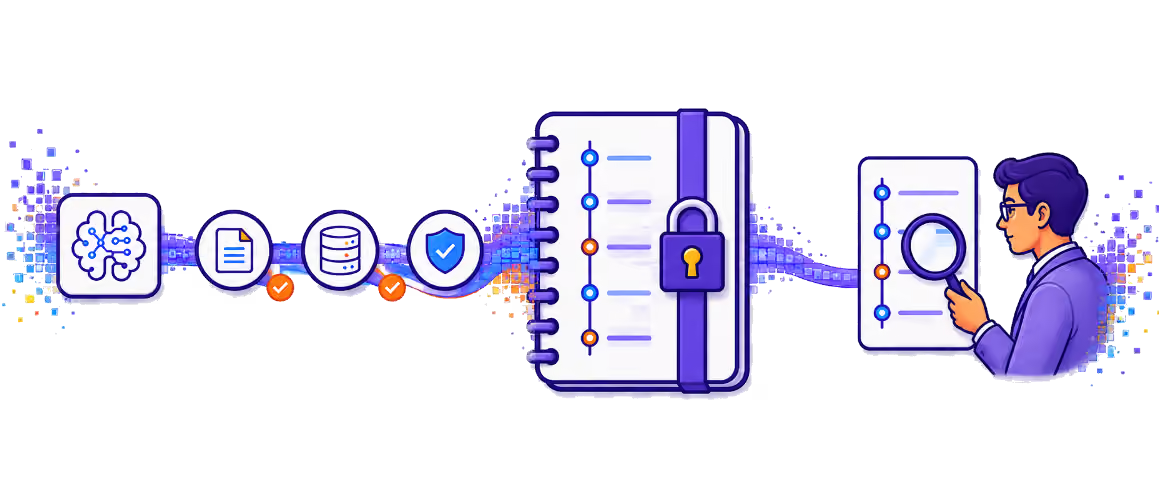
When a financial agent's action is questioned, a bank needs evidence connecting the agent, the user it represented, the tools it called, and the controls applied. Application logs often capture only fragments. PointGuard AI correlates agent telemetry and tamper-evident action records, helping security, risk, and compliance teams reconstruct activity across multi-step financial workflows.
Fragmented logs make it difficult to explain how an agent action occurred and which controls governed it.
Agent Observability correlates Agent Mission Control and MCP Security Gateway telemetry into an operational record that supports investigation and oversight.
1. Capture workflow activity. Collect OpenTelemetry-compatible traces for agent actions, tool interactions, handoffs, and enforcement events. Preserve the relevant operational context across the parts of a governed workflow.
2. Attribute actions to identities. Connect activity to verified agents, human owners, and delegated user authority. Use cryptographically attributed action records to distinguish who requested an operation from which agent executed it.
3. Reconstruct the decision path. Trace policy results, guardrail findings, approvals, and containment events alongside tool activity. Show the sequence of observable decisions without relying on an unsupported reconstruction of a model's internal reasoning.
4. Support continuing oversight. Use dashboards and investigation views to review violations, approvals, and policy effectiveness. Provide evidence for internal controls reviews and examiner inquiries about specific agent actions.