

Give every pipeline agent its own cryptographic identity so each build and deployment traces back to the agent that ran it.
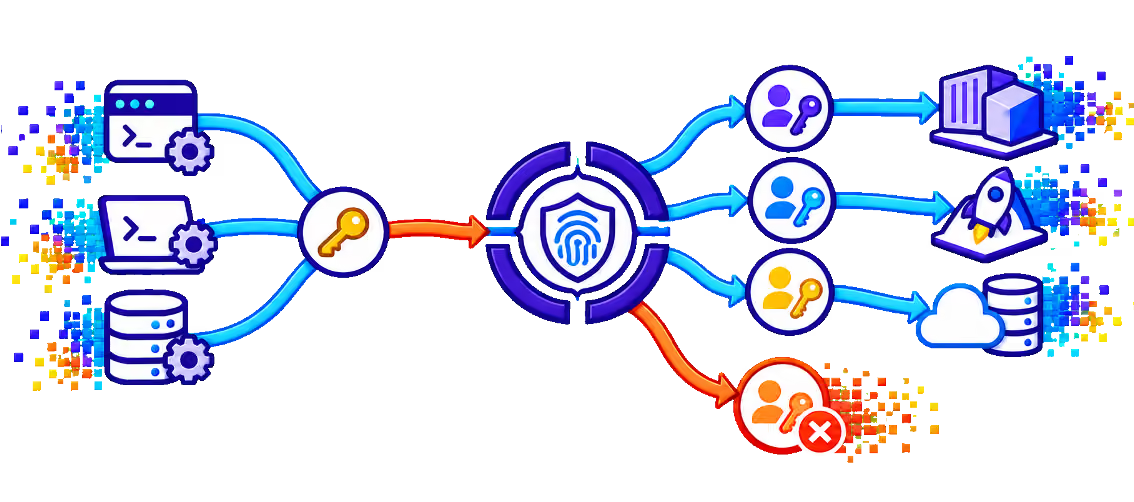
DevOps and coding agents in CI/CD pipelines often share generic API keys or inherit a developer's credentials. When something goes wrong, no build, commit, or deployment can be traced to the agent that made it, and revoking access means breaking every pipeline at once. PointGuard AI issues each agent a unique, verifiable identity so teams can authenticate, attribute, and revoke agents individually.
Shared credentials make pipeline agents anonymous and hard to contain.
Agent Identity & Access Security assigns verifiable identities and replaces shared credentials with scoped, short-lived access.
1. Register every pipeline agent. Assign each agent a DID-based identity backed by Ed25519 keys, with a named owner and defined purpose.
2. Replace shared secrets. Issue short-lived, scoped tokens through OAuth 2.0 and broker remaining secrets through HashiCorp Vault, AWS Secrets Manager, or Azure Key Vault.
3. Delegate with context. Use On-Behalf-Of tokens when an agent acts for a developer, so actions carry both identities.
4. Attribute and revoke. Tie every build, commit, and deployment to its agent identity. Revoke a single agent instantly without disrupting others.