

Scope agent access to retailer POS and partner data with per-agent, per-tool authorization at a central policy enforcement point.
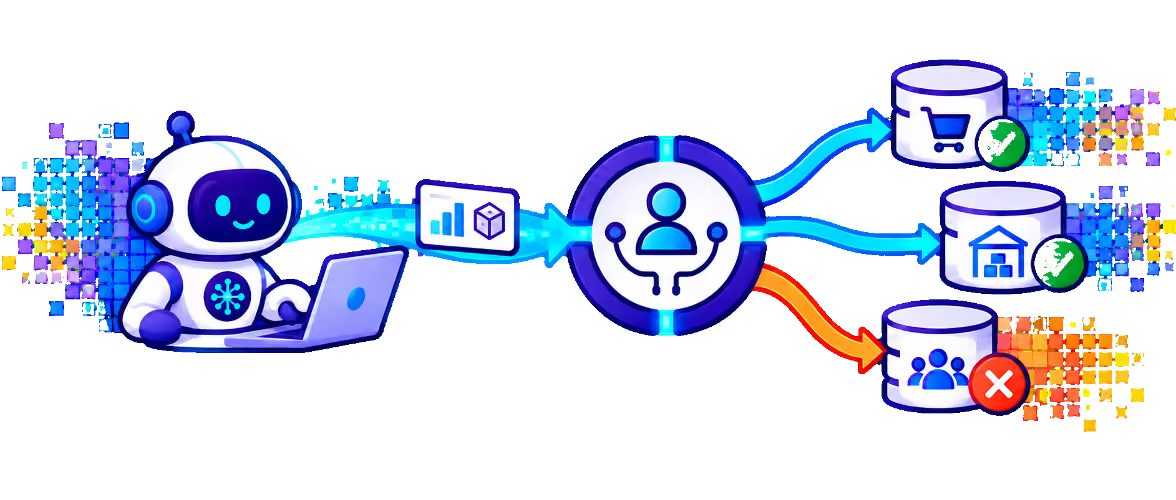
Agents that sync forecasts and promotions pull data from retailer POS, inventory, and partner portals through MCP servers and APIs. These connections often carry sweeping default access, so one manipulated agent can read or change far more partner data than its task requires and breach data-sharing agreements. PointGuard AI enforces fine-grained authorization on every governed tool call.
Partner data connections grant more access than agents need.
MCP Security Gateway and Agent Identity & Access Security authorize and log every partner data call.
1. Inventory connections. Identify agents, MCP servers, and the retailer systems they reach.
2. Authorize every call. Enforce per-agent, per-tool, per-operation policies at a centralized policy enforcement point.
3. Respect data agreements. Restrict access by retailer, category, and data type to match partner terms.
4. Log and review. Record every call and decision for partner reviews and audits.