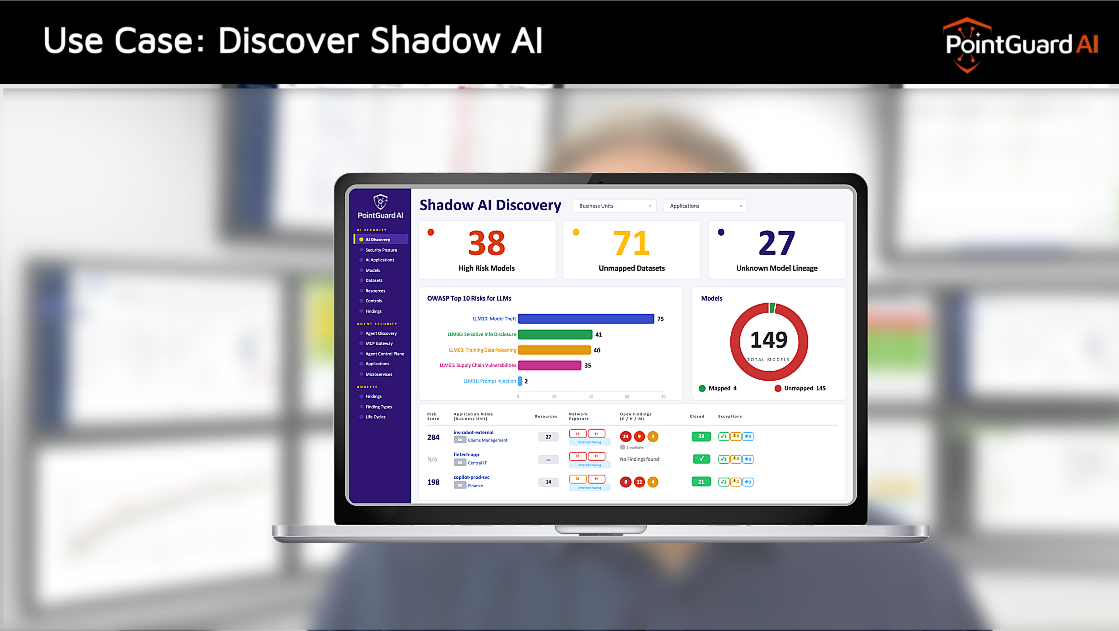
Continuously discover, inventory, and assess unknown AI resources across enterprise environments.
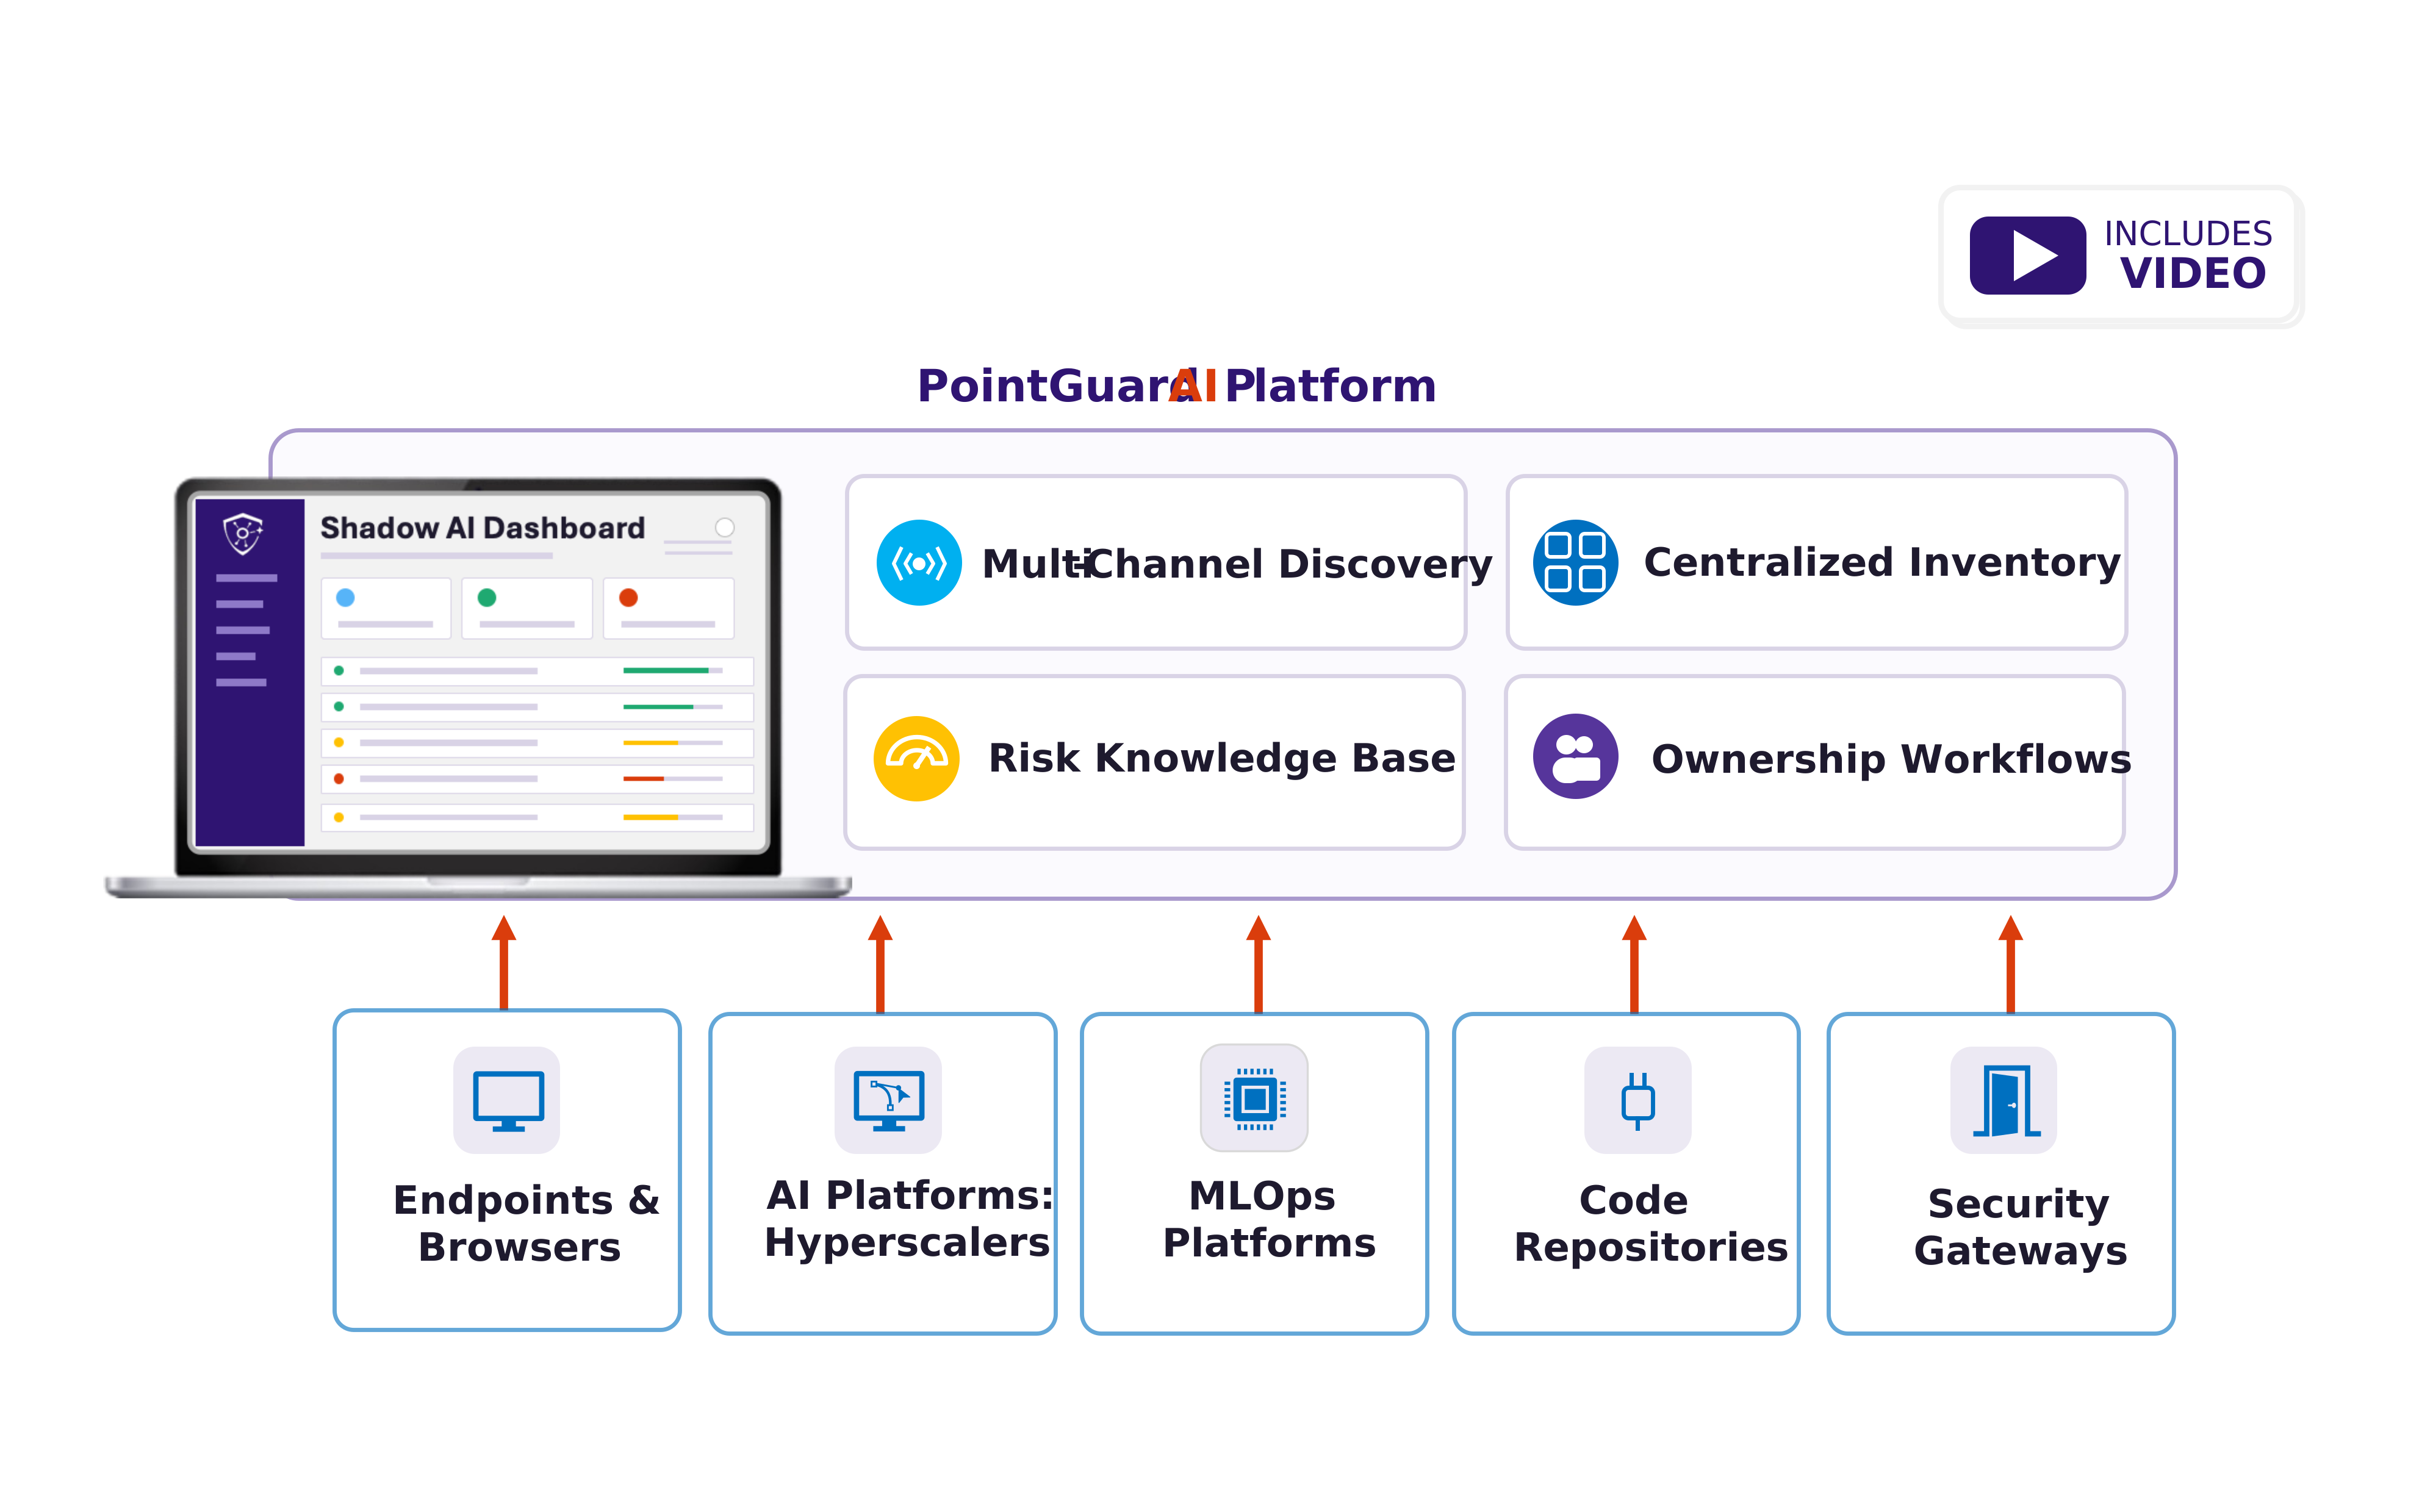
Continuously identify unknown AI applications, models, agents, MCP servers, and connected services wherever they appear. Correlate each discovery with ownership, usage, provenance, and risk intelligence so security teams can govern AI adoption without relying on incomplete manual inventories.
Shadow AI now extends far beyond unapproved chatbots. AI resources can enter through employee endpoints, coding assistants, development platforms, open-source repositories, agent frameworks, and MCP infrastructure, creating several recurring challenges:
PointGuard AI provides a comprehensive solution that turns Shadow AI discovery into a continuous risk and governance workflow:
1. Discover AI across the enterprise. Use AI Discovery & Inventory and Workforce AI Usage Control to identify models, agents, applications, MCP assets, and external services across code, platforms, endpoints, and runtime activity.
2. Build a dynamic inventory. Consolidate discoveries into a current system of record with ownership, business purpose, connected applications, approval status, and lifecycle context.
3. Assess component risk. Apply PointGuard AI risk intelligence to evaluate open-source models and MCP servers for security, operational controls, provenance, and adoption maturity.
4. Route assets into governance. Use AI Governance workflows to review, approve, restrict, investigate, or remediate newly discovered resources based on policy and risk.
This approach creates a continuous path from discovery to risk assessment, accountability, and enterprise governance.
The solution addresses these OWASP and NIST threat controls:

Learn More
Customers
AI Security Incidents